
Investors hit by Moldovan leak of BRS data lose out on compensation, ODPC says
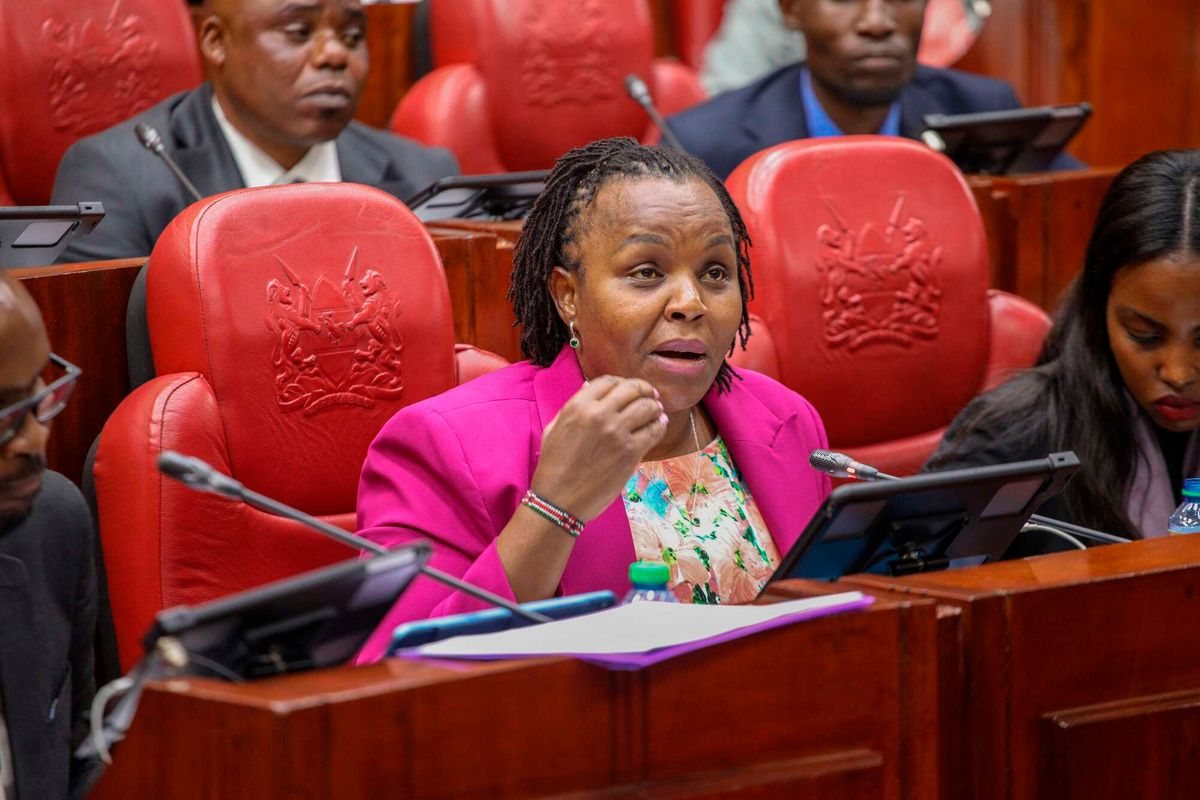
Kenyan investors whose company ownership details were exposed online by a Moldovan firm will receive no compensation because none of them lodged a complaint with the data regulator, according to Business Daily.
The Office of the Data Protection Commissioner (ODPC) has closed its investigation into the breach at the State-owned Business Registration Service (BRS). The regulator said the Moldovan company involved agreed to delete the data and no affected party filed a complaint against BRS.
Business Daily reports that the absence of claims spared the agency from paying out billions of shillings in compensation.
How the breach happened
B2bhint, a company based in Moldova, exploited a bug in the BRS IT system in February last year. It gained access to sensitive records on significant shareholders in registered firms, including names of beneficial owners, residential addresses, email addresses and phone numbers.
The information related to more than two million registered businesses, among them firms linked to President William Ruto, the Kenyatta family, former Prime Minister Raila Odinga and other prominent investors.
According to the report, the leak covered:
- 812,863 phone numbers
- 832,648 email addresses
- 2,091,046 physical addresses
- the status of 2,093,194 firms
Beneficial ownership details are not intended for public view and have largely been available only to law enforcement agencies. The breach left business owners and company officials exposed to identity theft, extortion, fraud and other abuse.
B2bhint was selling more than eight million items of data, at prices ranging from about two shillings for a phone number to Sh24 million for a package. Business Daily estimates the value of the stolen data at Sh2.4 billion. The firm denied hacking BRS, instead blaming weak cybersecurity for allowing it easy access.
Regulator explains decision
The ODPC opened the probe on its own initiative, without a complaint from any party, to determine whether BRS had broken the Data Protection Act and negligently exposed user information.
Data Commissioner Immaculate Kassait told Business Daily that compensation could not be awarded because no one sought it.
"Nobody came to say, 'This is my data that was breached'," Ms Kassait said.
She explained that the regulator issued BRS with an enforcement notice requiring it to strengthen its data protection systems. Because the agency complied, there was no need to escalate to a penalty notice, which would have carried a financial sanction.
Under the Data Protection Act, 2019, the ODPC can impose administrative fines of up to Sh5 million. Affected individuals are also entitled to compensation under the law, but Ms Kassait said BRS leak victims will get nothing as none came forward.
International practice
Business Daily notes that, globally, compensation for data breach victims typically follows legal claims brought by those affected. It cites American telecoms firm AT&T, which in 2024 paid some customers between $2,500 (Sh325,125) and $5,000 (Sh650,250) following a class-action suit over a March 2024 breach.
In Kenya, the ODPC has in recent times ordered multi-million shilling awards to individuals over mishandling of personal data, with firms ranging from hotels to tech companies and micro-lenders required to meet data handling standards.
Data deleted after cross-border effort
Kenya secured the deletion of the stolen information through a deal with the Moldovan firm, ending an 18-month probe into what the publication describes as the largest data breach involving a government entity in the country's history.
The government drew on the support of the European Union Commission and Moldova's data protection authority to trace the company and compel it to erase the data.
This story was prepared by the Hamasta Newsdesk with AI assistance, based on reporting by Business Daily. Read the original report. Photo: Business Daily.


Know what people say about you.
Media monitoring, audience insights and strategic communication for your brand.


More in Business
See all
KUSCCO Mutual Assurance Statutory Management Extended to December 31
Equity Group nine-month profit rises 32pc to Sh71.5bn on income growth
Treasury Proposes Car Loan and Mortgage Fund for TSC Secretariat Staff
Nigerian fintech Payaza enters Kenya after securing CBK payment licence
Family Bank nine-month profit jumps 69pc to Sh6.07bn on stronger lending
Global Community Remarks
0